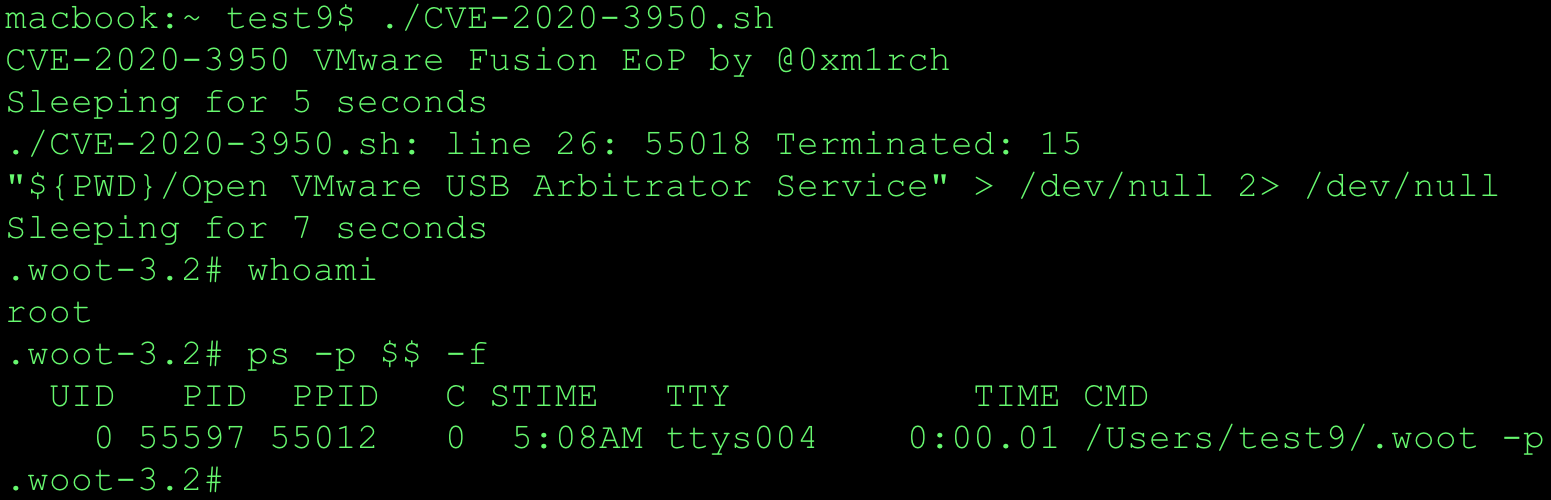
VMware Fusion 11.5.12 and prior are vulnerable to an elevation of privilege vulnerability. For more details please review the advisory and proof of concept on my GitHub page CVE-2020-3950.sh. VMware released the patch last week and a public advisory VMSA-2020-0005 today however it has been determined that the patch does not properly fix the vulnerability. I reached out to the VMware security team and received a response at 10:31 UTC 2020-03-18 - “We are aware of the situation and working on the next steps”.
I also learned today that Jeff Ball at GRIMM also independently discovered and reported the vulnerability to VMware. This is a first for me. Make sure to read their excellent detailed write-up https://github.com/grimm-co/NotQuite0DayFriday/tree/master/2020.03.17-vmware-fusion. You can also follow the thread on Twitter.
https://twitter.com/0xm1rch/status/1240030085450731521?s=20
Related Articles
- BleepingComputer VMware Fixes High Severity Privilege Escalation Bug in Fusion
- ZDNet VMware patches privilege escalation vulnerability in Fusion, Horizon
- SecurityWeek VMware Fixes Privilege Escalation Vulnerability in Fusion for Mac
- SecurityWeek Patch for Recently Disclosed VMware Fusion Vulnerability Incomplete
- SecurityWeek VMware Again Fails to Patch Privilege Escalation Vulnerability in Fusion
- Metasploit Module VMware Fusion USB Arbitrator Setuid Privilege Escalation